Triple ISO Certified · Sovereign Enclave Architecture · AWS Technology Partner

The Autonomous Software Portfolio
for the Governed Enterprise.

Eight targeted platforms engineered for autonomous security operations, deterministic identity execution, cloud economics, and hybrid network infrastructure. Deployed strictly inside your perimeter with zero telemetry egress and cryptographic evidence attached.

8 PlatformsUnified Sovereign CoreOne governed engine powers 8 autonomous enterprise revenue lines
3–10 sAutonomous TriageMulti-agent correlation replaces 45-minute tier-1 triage queues
100% In-BoundaryZero Telemetry TransitRuns inside client VPC, on-premise, or air-gapped enclaves
CryptographicTamper-Evident ProofAppend-only hash-chained evidence ledger attached to every step
Enterprise software portfolio

Eight autonomous platforms. One governed core.

Review live operational capabilities across Cybersecurity, Cloud Operations, Observability, and the Sovereign Foundation. Filter by domain or explore each platform's architecture.

Cybersecurity · 01FLAGSHIP
01 · Live triage

Trace8 AIR™

Autonomous Security Operations

The Autonomous Agentic Operating System for Enterprise SOCs

Autonomous multi-agent investigation over existing SIEM telemetry. Correlates attack edges and delivers analyst-verified containment in 3–10 seconds with zero duplicate ingestion fees.
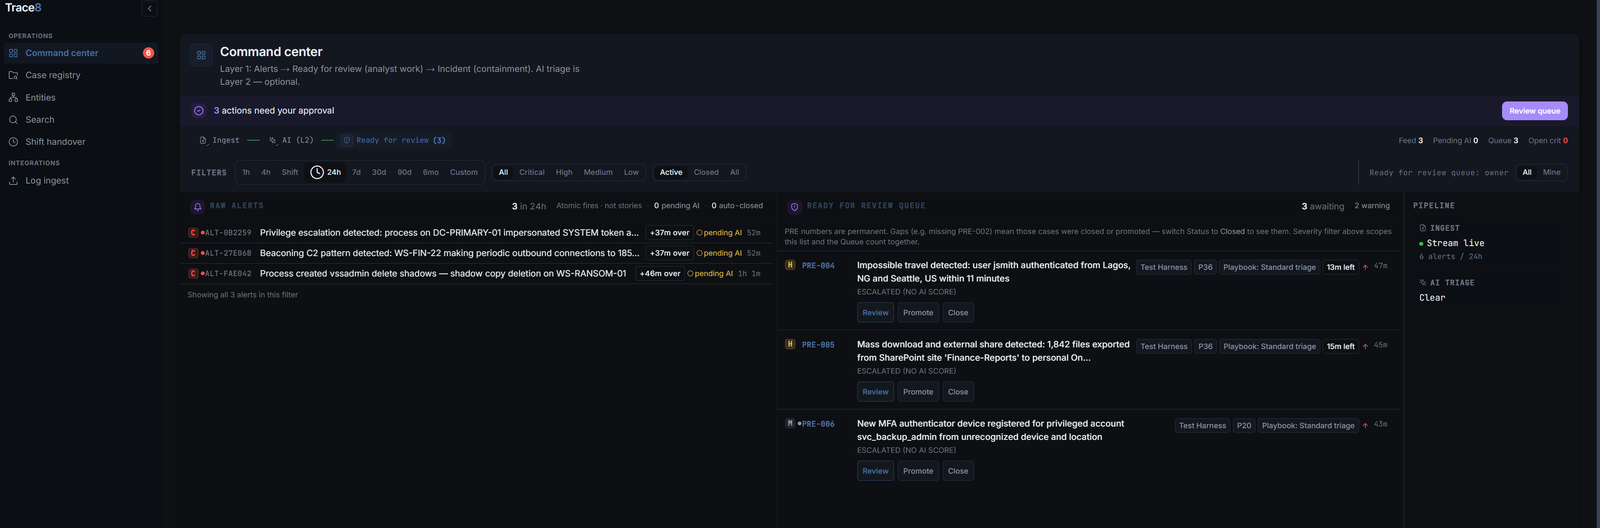
  • Specialist investigation agents correlate attack path edges & blast radius in seconds
  • Federated query mode over Microsoft Sentinel, Splunk & Elastic without second index fees
  • Sovereign validation freeze gates enforce explicit human sign-off for destructive containment
  • In-tenant ephemeral memory lifecycle with zero raw customer telemetry replication
Microsoft SentinelSplunk ESElastic SecurityCrowdStrike FalconEntra ID
🛡️Triple ISO 27001 · Cryptographic Proof Ledger
Cybersecurity · 02PATENT PENDING
02 · Identity execution

Cube23™

Deterministic Identity Execution

Zero Standing Privileges with Cryptographic State Synchronization

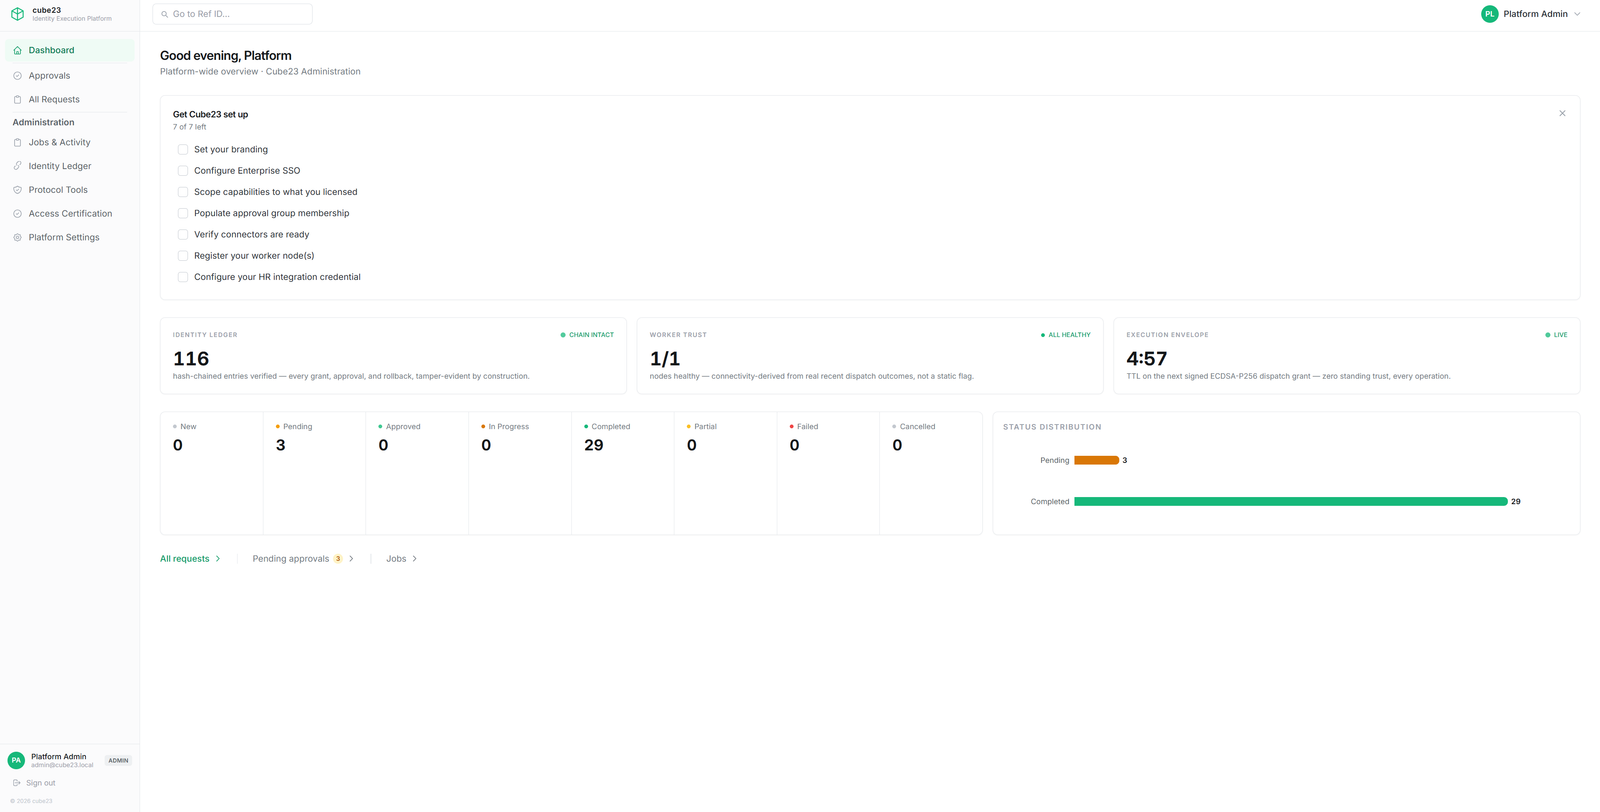
Deterministic joiner-mover-leaver synchronization and ephemeral micro-TTL credentials. Eliminates identity sprawl and privilege accumulation across hybrid cloud estates.

  • Signed ECDSA-P256 execution envelopes enforce micro-TTLs for trusted worker nodes
  • Append-only SHA-256 hash-chained ledger generates undeniable audit proof for every event
  • Live fan-out queries construct a real-time digital twin across all connected directories
  • Synchronizes complex joiner-mover-leaver operations across identity silos in under 3 minutes
Active DirectoryEntra IDCyberArk PAMAWS IAMServiceNowWorkday
🛡️Triple ISO 27001 · Cryptographic Proof Ledger
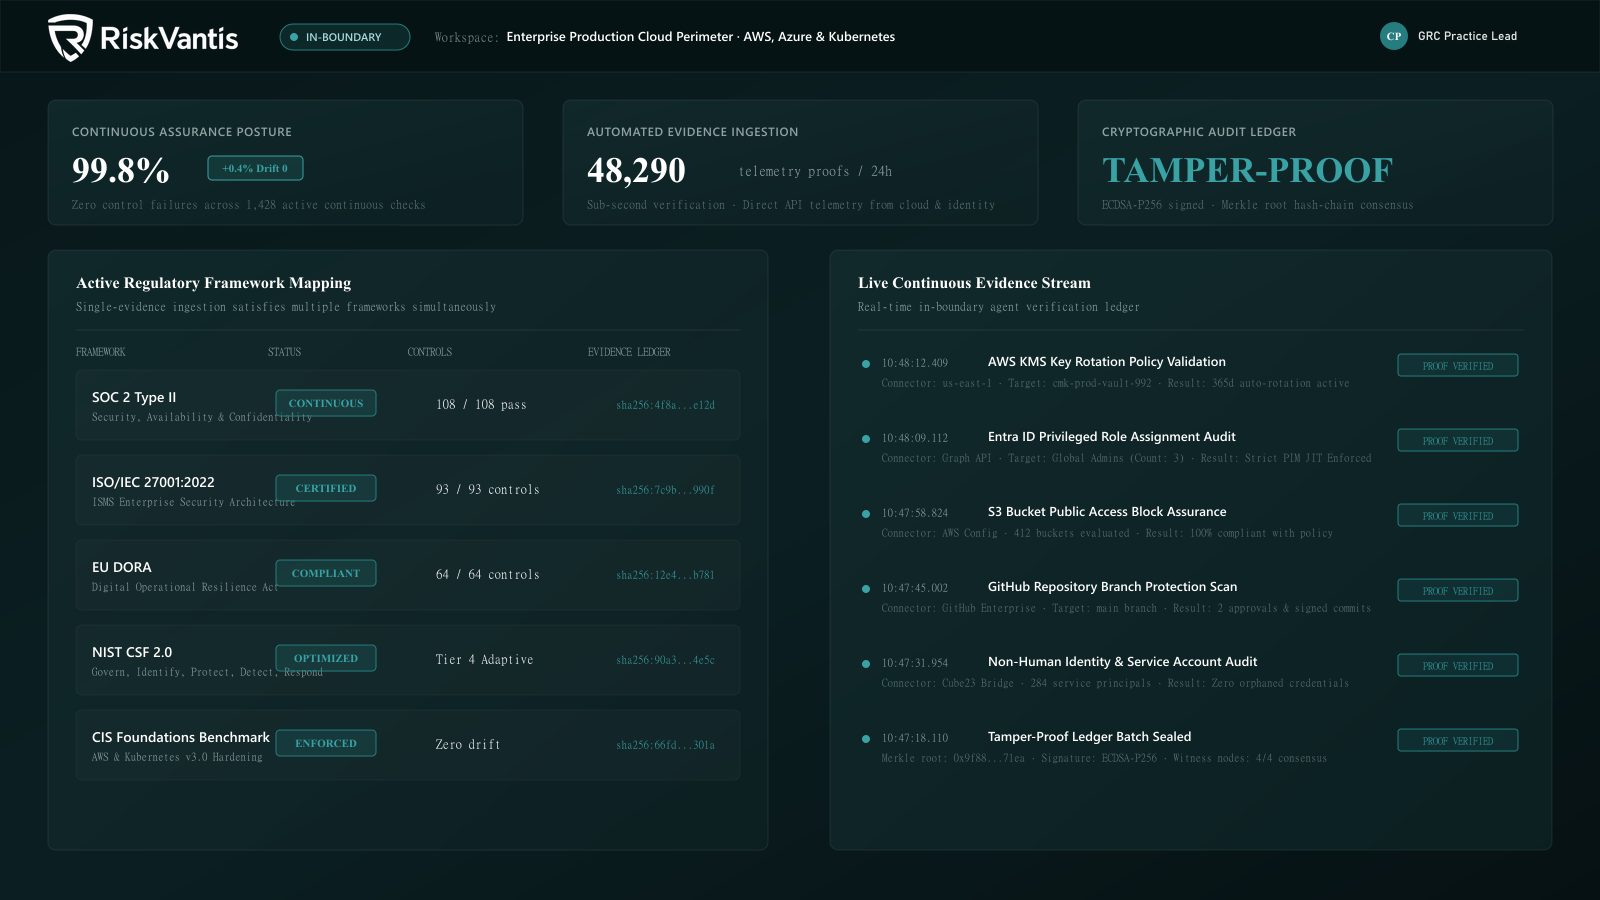
Cybersecurity · 03CONTINUOUS GRC
03 · Continuous assurance

RiskVantis™

Continuous Governance & Assurance

Autonomous Control Evidence Compilation Across SOC 2, ISO & DORA

Continuous automated control testing and real-time evidence compilation across SOC 2 Type II, ISO 27001, and DORA. Replaces annual audit fire drills with living cryptographic compliance ledgers.

  • 24×7 automated evidence gathering across cloud, container, and identity telemetry
  • Pre-mapped audit frameworks for SOC 2, ISO 27001, NIST CSF, and EU DORA mandates
  • Real-time drift alerts detect security configuration anomalies before external audits
  • Automated evidence chain validation generates certified auditor-ready export packages
AWS OrganizationsAzure MonitorGoogle CloudJira SoftwareServiceNow GRC
🛡️Triple ISO 27001 · Cryptographic Proof Ledger
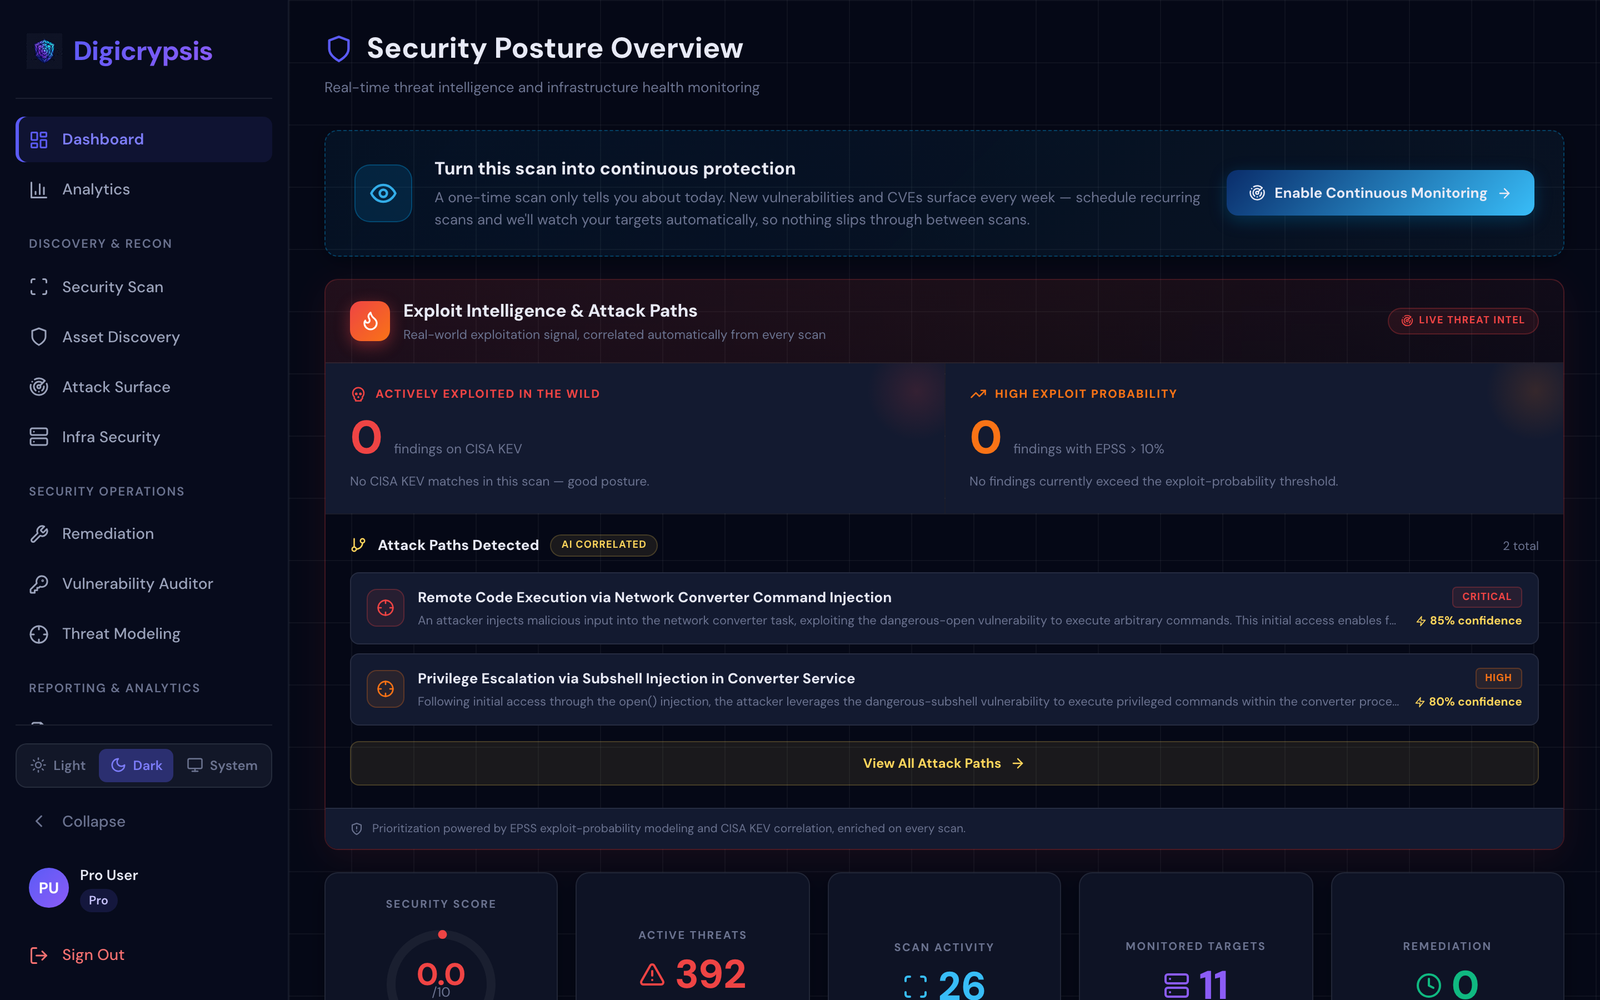
Cybersecurity · 04APPSEC
04 · Code diagnostics

Digicrypsis™

Autonomous Source Intelligence

Compiler-Grade Code Vulnerability Diagnostics & Verified Remediation

Autonomous single-pass code vulnerability diagnostics and compiler-grade remediation verification. Analyzes abstract syntax trees and generates verified pull requests without false positives.

  • Semantic AST taint analysis detects deep-rooted business logic vulnerabilities
  • Autonomous zero-hallucination patch generation verified against internal test suites
  • Automated pull request creation integrates directly into CI/CD developer workflows
  • Comprehensive Software Bill of Materials (SBOM) and third-party dependency provenance
GitHub EnterpriseGitLab CIBitbucketJenkinsSonarQubeSnyk
🛡️Triple ISO 27001 · Cryptographic Proof Ledger
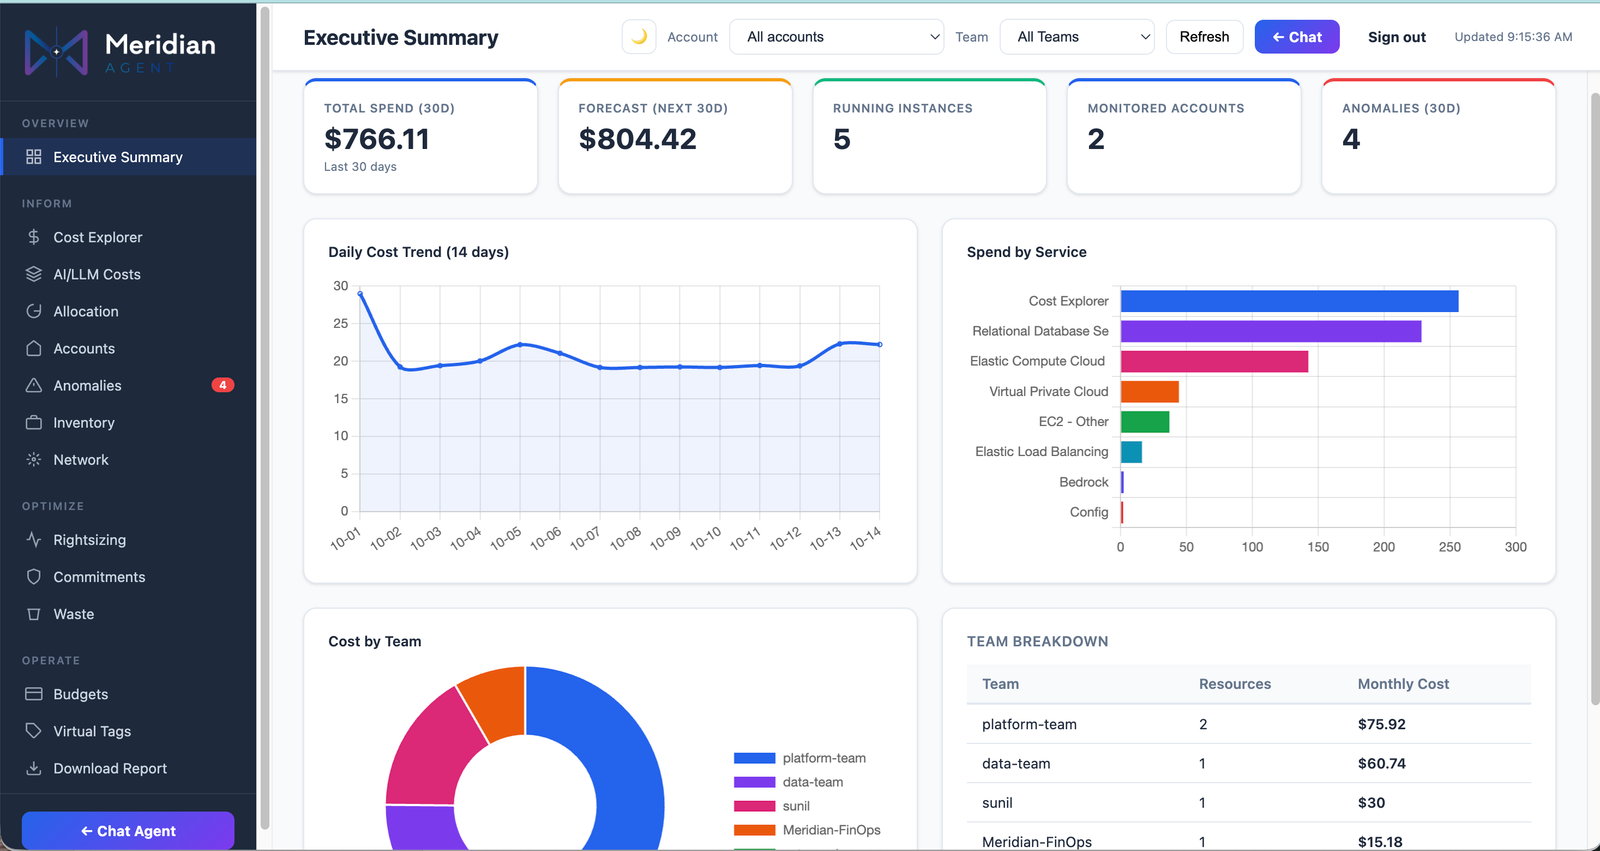
Cloud Operations · 05AWS WELL-ARCHITECTED
05 · Cloud economics

Meridian FinOps™

Autonomous Cloud Cost Intelligence

Continuous Cloud Cost Intelligence Paired with Pre-Generated Terraform

Continuous cloud cost intelligence pairing named enterprise architects with pre-generated Terraform remediation. Reclaims 20–40% unallocated cloud spend without production downtime.

  • Real-time waste detection across idle compute, orphaned volumes, and over-provisioned DBs
  • Pre-generated Terraform & OpenTofu pull requests with zero manual configuration required
  • Deterministic root-cause attribution links anomalous spend spikes to responsible teams
  • Multi-cloud unit economics tracking across AWS, Azure, GCP, and Kubernetes clusters
AWS Cost ExplorerAzure Cost ManagementGCP BillingTerraformDatadog
🛡️Triple ISO 27001 · Cryptographic Proof Ledger
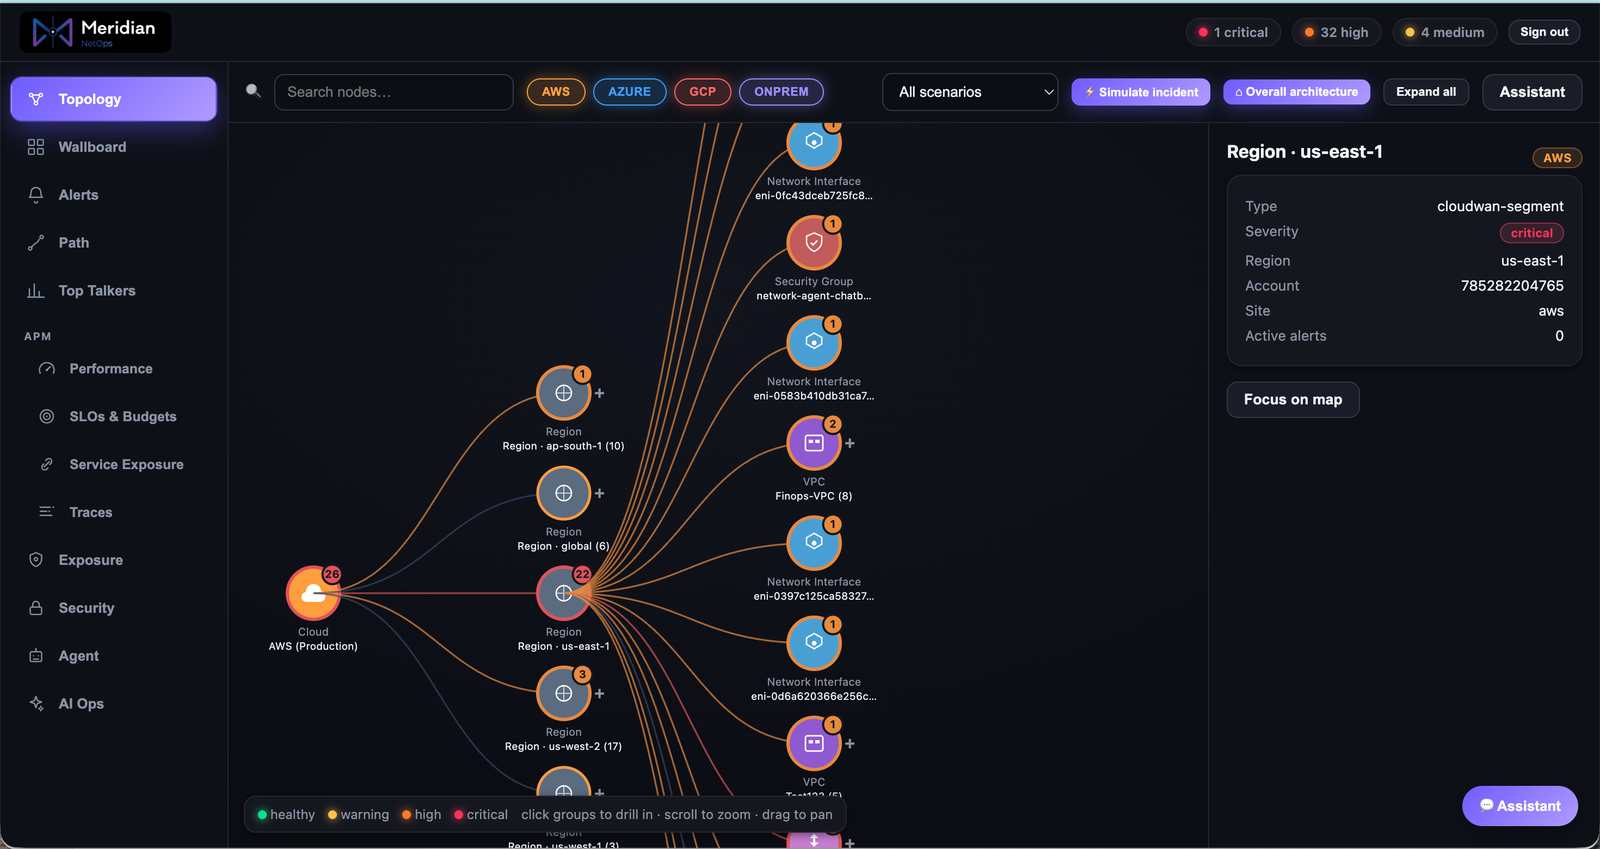
Cloud Operations · 06CLOUD WAN
06 · Network operations

Meridian NetOps™

Autonomous Hybrid WAN & Network Operations

Software-Defined Hybrid WAN Monitoring & Automated Route Troubleshooting

Software-defined hybrid WAN monitoring, automated BGP routing troubleshooting, and circuit failover orchestration across enterprise data centers, branch sites, and public clouds.

  • Sub-second detection of BGP route flapping, asymmetric paths, and latency anomalies
  • End-to-end synthetic probing correlates cross-cloud transit gateways with direct circuits
  • Autonomous remediation runbooks execute deterministic circuit rerouting under policy gates
  • Unified topology map correlates physical data centers with SD-WAN and cloud perimeters
Cisco SD-WANArista NetworksJuniper NetworksAWS DirectConnectAzure ExpressRoute
🛡️Triple ISO 27001 · Cryptographic Proof Ledger
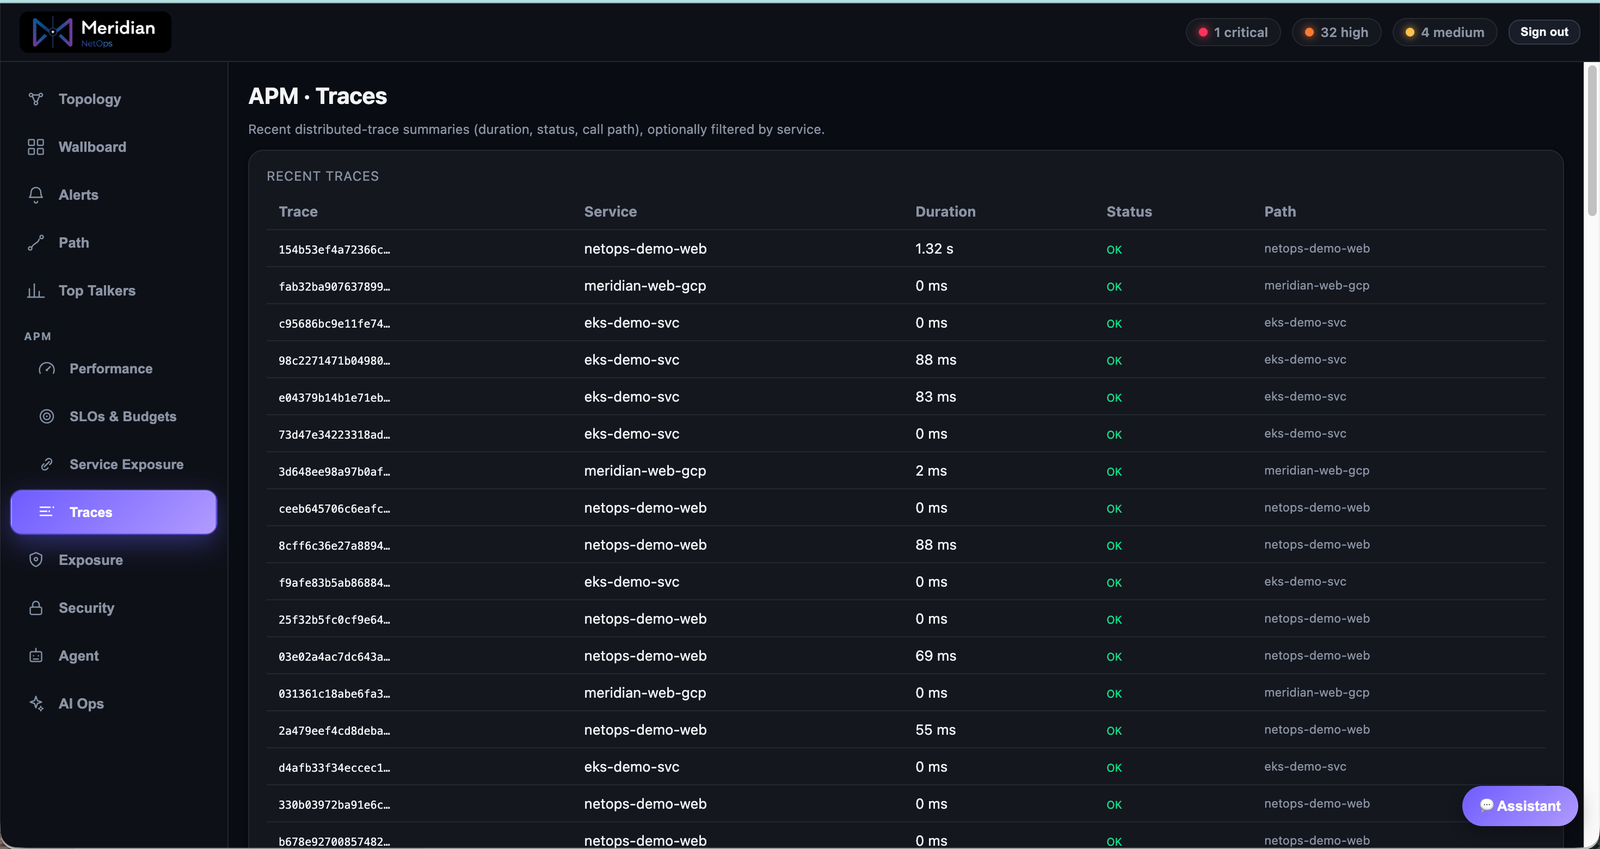
Application Performance · 07OBSERVABILITY
07 · Distributed APM

Meridian APM™

Distributed Observability & Tracing

OpenTelemetry-Native Transaction Tracing Linked to Network Topologies

Autonomous transaction tracing and bottleneck localization across microservices and legacy core systems. Correlates distributed traces directly to underlying cloud network paths.

  • 100% OpenTelemetry native telemetry collection with zero proprietary agent lock-in
  • Autonomous bottleneck localization traces slow database queries and microservice latency
  • Unified service graph correlates distributed application calls with cloud network topologies
  • Dynamic SLO/SLA budget tracking triggers automated diagnostic snapshots during incidents
KubernetesOpenTelemetry SDKsPrometheusEnvoy ProxyPostgreSQLKafka
🛡️Triple ISO 27001 · Cryptographic Proof Ledger
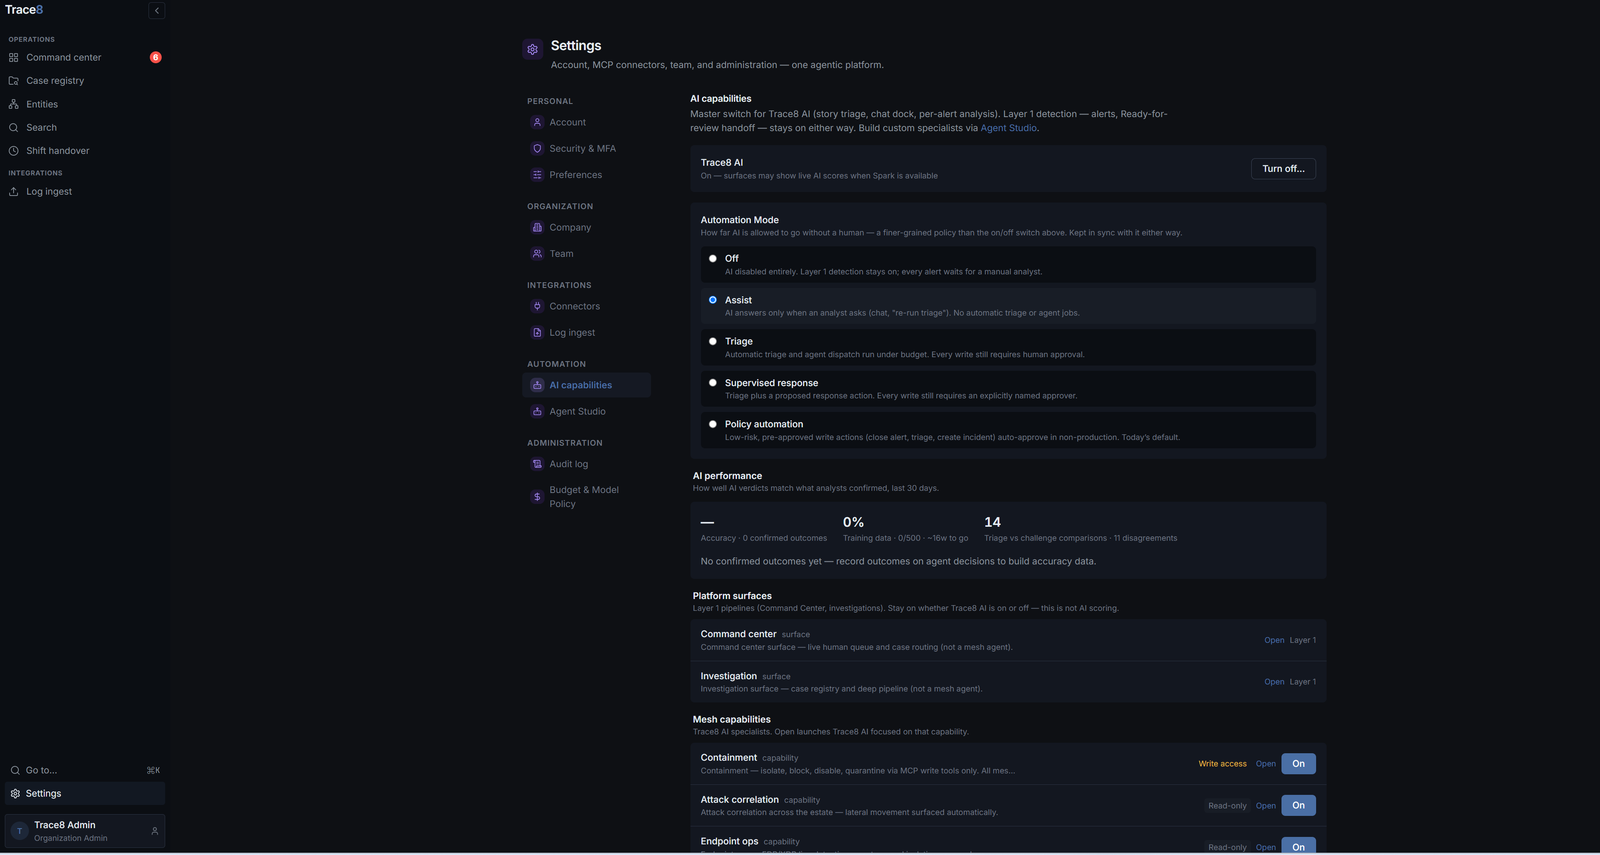
Foundation · 08SOVEREIGN CORE
08 · Execution layer

The CAELION Harness™

The Governed Execution Core

The Sovereign Substrate Enforcing Ephemeral Credentials & Freeze Gates

The shared governed core that every CAELION software product executes on. Enforces ephemeral read-only credentials, sovereign validation freeze gates, and tamper-evident audit ledgers.

  • Sovereign validation freeze gates halt all destructive actions until authorized human sign-off
  • Micro-TTL credentials generated on-the-fly and destroyed immediately following task completion
  • Append-only ECDSA-P256 cryptographic evidence ledger creates immutable audit proof
  • Model-agnostic substrate: interchangeable across AWS Bedrock, Claude, OpenAI, and local LLMs
Any Cloud VPCOn-Premises Bare MetalAir-Gapped Sovereign EnclavesHashiCorp Vault
🛡️Triple ISO 27001 · Cryptographic Proof Ledger
THE SHARED GOVERNANCE CORE · THE CAELION HARNESS™

Models Are Commodities.
Governed Systems Are Not.

Every CAELION software product executes on The Harness. Foundation models will continue to progress rapidly toward commoditization, but enterprises cannot run raw models against production workloads without strict security boundaries, ephemeral credential isolation, and tamper-evident audit ledgers.

01

Zero Telemetry Transit

Customer telemetry, private code, and identity metadata stay inside your perimeter. No external log shipping, no third-party training.

02

Validation Freeze Gates

Destructive maneuvers (account lockout, IP isolation, terraform apply) freeze at sovereign gates requiring explicit human sign-off.

03

Hash-Chained Audit Ledger

Every prompt, model reasoning step, and analyst approval is hashed with ECDSA-P256 proof, creating undeniable audit compliance.

04

Model-Agnostic Substrate

Seamlessly interchangeable across AWS Bedrock, Anthropic Claude, OpenAI, or local open-weights inside air-gapped enclaves.

Architectural comparison

How CAELION Autonomous Platforms Compare

Enterprise software engineered for organizations transitioning away from high-friction human outsourcing and rigid legacy point tools.

Architectural Dimension
AUTONOMOUS SOFTWARECAELION Platforms
Traditional Outsourcers & MSPsLegacy Point Security / IT Tools
Execution Model
Autonomous multi-agent execution inside your boundary with sub-second response
Manual offshore labor with multi-day ticket queues and human rework lagStatic dashboards requiring manual analyst triage across disconnected consoles
Telemetry Sovereignty
100% in-tenant sovereign; zero customer data replication or external transit
Customer data copied to offshore hubs with high compliance & leakage riskRequires multi-TB log ingestion into proprietary vendor cloud multi-tenant indexes
Safety & Governance
Sovereign validation freeze gates require explicit human sign-off for critical actions
Opaque manual procedures prone to human oversight and unauthorized commandsUngoverned automation scripts or completely manual analyst intervention
Verification & Audit
Append-only SHA-256 hash-chained ledger with cryptographic receipts for regulators
Subjective timesheets and manual spreadsheets compiled for periodic auditsDisjointed syslog fragments requiring weeks of retrospective forensic aggregation
Deployment Flexibility
Deployable inside customer VPC, on-premise, or air-gapped with local LLM weights
Fixed offshore facilities with high switching barriers and rigid SLAsVendor cloud lock-in with mandatory internet telemetry egress
Enterprise inquiries

Frequently Asked Questions

Technical and commercial details regarding deployment boundaries, compliance standards, and proofs of concept.

Can CAELION platforms deploy into our private VPC or air-gapped sovereign cloud?

Yes. Every CAELION platform is engineered from the ground up for sovereign in-boundary deployment. Software packages can run directly inside your AWS, Azure, or GCP perimeter, on-premises bare-metal infrastructure, or completely air-gapped environments utilizing local open-weight models. Zero raw customer telemetry or confidential data ever leaves your security boundary.

Do CAELION products require replacing our existing SIEM, IAM, or monitoring tools?

No. CAELION platforms operate as an autonomous intelligence and execution layer on top of your existing enterprise investments. For example, Trace8 AIR federates directly over Microsoft Sentinel, Splunk, or Elastic via read-only queries with zero duplicate ingestion fees. Cube23 synchronizes across Active Directory, Entra ID, and CyberArk without ripping out your current directory backbones.

How do sovereign validation freeze gates ensure system safety during autonomous actions?

While triage, correlation, and diagnostic analysis complete autonomously in seconds, any potentially destructive maneuver (such as isolating an IP, disabling a privileged credential, or rerouting network traffic) halts at a deterministic validation gate. The platform presents a cryptographic evidence dossier to an authorized human analyst who must explicitly review and sign off before execution proceeds.

What is the difference between The CAELION Harness and commodity AI frameworks?

Commodity frameworks (like LangChain or raw foundation model APIs) lack enterprise-grade security boundaries, credential isolation, and auditability. The CAELION Harness provides the durable systems moat: scoped micro-TTL credentials, deterministic validation freeze gates, multi-tenant isolation, and append-only cryptographic evidence ledgers that satisfy strict global regulatory standards like SOC 2, ISO 27001, and DORA.

How does a 30-day proof-of-concept (POC) work on enterprise data?

We deploy a sandboxed, read-only instance of the selected platform directly inside your enterprise cloud boundary or lab environment. Under strict NDA and enterprise governance, we demonstrate governed autonomous agents resolving real alerts, optimizing actual cloud spend, or synchronizing live identity workflows. Most organizations achieve measurable ROI validation within the first 14 days.

Proof on actual workloads

See governed autonomous software running inside your perimeter

Bring us an alert queue, an identity directory, or an AWS account. In a private architecture discovery session under NDA, we'll run autonomous agents against it with read-only credentials and cryptographic proof attached.